

EDI compliance means exchanging electronic business documents in the standards, formats, timeframes and security conditions your trading partners require. Being EDI compliant means your purchase orders, invoices, shipment notices and other transactions pass your partner's validation the first time, with no rejections, rework or chargebacks.
For suppliers, EDI compliance is rarely optional. Retailers, healthcare payers and logistics providers set their own EDI requirements and enforce them with scorecards and penalties. This guide explains what EDI compliance involves, what the requirements look like in practice, and the steps to become EDI compliant.
EDI Compliance at a Glance
What it is: Meeting the standards, formats, timing and security rules your trading partners set for every EDI document you exchange.
Who it applies to: Suppliers, manufacturers, carriers, healthcare providers and anyone who trades documents electronically with larger partners.
What it protects: Revenue and relationships, by avoiding rejected documents, delayed payments, chargebacks and manual rework.
How to achieve it: Get each partner's specification, map your data, test, validate, acknowledge and monitor continuously.
What Is EDI Compliance?
EDI compliance is the practice of meeting the rules that govern how business documents are exchanged through electronic data interchange (EDI). Those rules come from two places: the EDI standard itself, such as ANSI X12 or EDIFACT, and the specific implementation guide each trading partner publishes on top of it.
A document can be valid under the standard and still be non-compliant with a partner's specification. For example, a partner may require a particular qualifier, a certain date format or an extra reference number that the base standard treats as optional. Compliance means meeting both layers.
Types of EDI Compliance
"EDI compliance" is not a single rulebook. Most organizations have to meet four different kinds of requirements at once:
Standards compliance: Your documents follow the syntax and structure of the chosen EDI standard, including correct envelopes, segment order and data types.
Trading partner compliance: Your documents meet the extra rules in each partner's implementation guide, such as required fields, code lists and business rules.
Regulatory compliance: Your transactions meet legal requirements in regulated industries, for example HIPAA for healthcare claims and eligibility.
Security and audit compliance: Your data is encrypted, access is controlled, and you can prove what was sent, received and acknowledged.
EDI Compliance by Standard
ANSI X12 is the most widely used EDI standard in North America. Compliance means using the agreed version (for example 004010 or 005010), the correct transaction set and the segment and element rules in the partner's guide.
EDIFACT is the international standard maintained under the United Nations and is common in global trade, customs and logistics. EDIFACT messages use different envelopes and message names than X12, so a mapping built for one cannot simply be reused for the other.
TRADACOMS is an older standard used mainly in UK retail. Some partners still require it, so suppliers that sell into that market may need to support it alongside X12 or EDIFACT.
What Does It Mean to Be EDI Compliant?
A business is EDI compliant when it consistently meets four conditions with each trading partner:
Standards and formats: Documents follow the agreed standard (ANSI X12, EDIFACT or TRADACOMS), version and segment structure.
Timeliness: Documents are sent within the partner's deadlines, for example an advance ship notice before the truck arrives, or an invoice within a set window.
Transmission and security: Data moves over the agreed channel, such as AS2, SFTP or a VAN, with the required encryption and acknowledgements.
Accuracy and acknowledgement: Data matches the underlying order, and the business sends and processes acknowledgements such as the 997 functional acknowledgement or the 824 application advice.
Because every partner can set different rules, a supplier with twenty customers may have twenty slightly different definitions of EDI compliant. That is why most compliance problems come from managing partner-specific specifications, not from the standards themselves.
It also helps to separate being EDI compliant from being certified. Certification is a one-time check, often run by a partner or a third party, that confirms your test documents meet their rules. Compliance is ongoing: it has to hold for every live document, and it can be lost when a partner updates its specification or when your own systems change.
EDI Compliance Requirements and Specifications
EDI requirements are usually documented in a partner's EDI specification, also called an implementation guide or mapping guide. A typical specification covers:
The transaction sets you must support, such as the EDI 850 purchase order and EDI 810 invoice
The standard and version, for example X12 004010 or 005010
Required, conditional and optional segments and elements
Allowed code values and qualifiers
Envelope identifiers (ISA/GS) and test versus production settings
Connection method, encryption and acknowledgement rules
Timing rules and penalties for late or invalid documents
For a closer look at the underlying formats, see our guide to EDI standards and the overview of common EDI transactions.
Specifications are not static. Partners add new required fields, retire old codes and move to newer standard versions. Treat the specification as a living document: record the version you built against, subscribe to partner notices, and re-test whenever a change is announced.
Common EDI Compliance Errors and How to Avoid Them
Most rejected documents fail for a small number of repeat reasons. Knowing them lets you build checks for each one before documents leave your system.
Missing required segments or elements: A field the partner marks as mandatory is blank. Fix it by validating required fields against the partner's guide before sending.
Wrong qualifiers or code values: A unit of measure, date qualifier or location code is not in the partner's allowed list. Keep a cross-reference table per partner.
Invalid dates, numbers or formats: A date is in the wrong format or a quantity has the wrong decimal precision. Enforce data types in the mapping.
Mismatched documents: The invoice does not match the purchase order or the advance ship notice. Compare quantities, prices and identifiers across related documents before release.
Duplicate or out-of-sequence control numbers: Interchange and group control numbers must be unique and ordered. Generate them centrally, not by hand.
Late documents: An advance ship notice arrives after the shipment, or an invoice misses the allowed window. Set alerts that fire before the deadline, not after.
Unprocessed acknowledgements: A 997 or 824 reports an error and nobody reads it. Route negative acknowledgements to a person or an automated retry.
Why EDI Compliance Matters
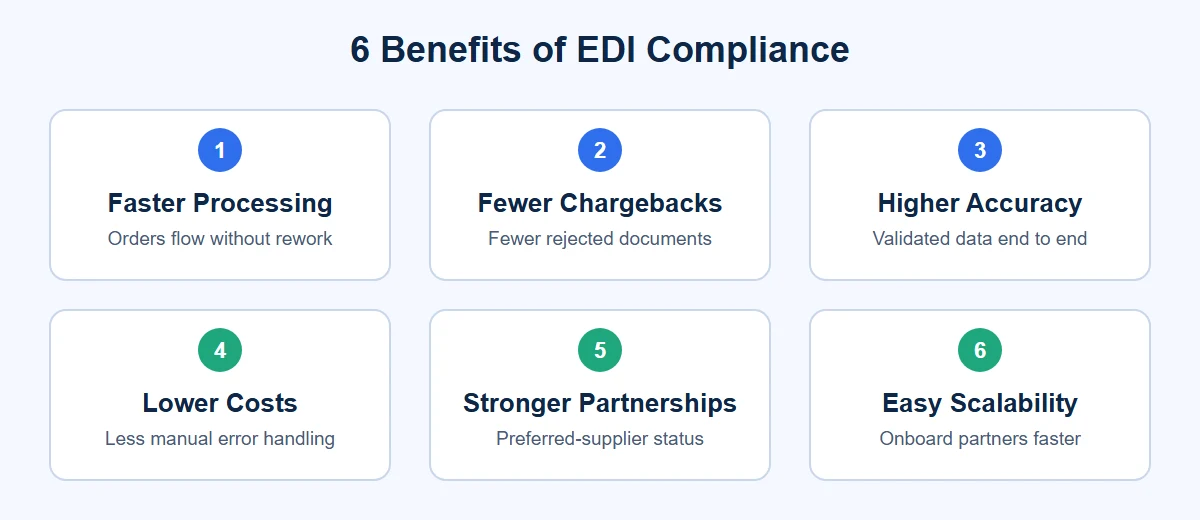
Non-compliant documents are rejected, delayed or flagged by your partner's system. Each exception takes manual work to find, fix and resend, and it can trigger financial penalties. The benefits of EDI compliance follow from avoiding that cycle:
Faster processing: Clean documents flow straight into your partner's order, warehouse and payment systems.
Fewer chargebacks and penalties: Retail and supplier programs often fine suppliers for late, missing or inaccurate documents, and compliant data avoids those fines.
Higher accuracy: Validation at the point of exchange catches errors before they become shipping or billing disputes.
Lower costs: Less manual exception handling means less staff time spent re-keying and resending documents.
Stronger partner relationships: Reliable, compliant suppliers are easier to work with and are more likely to keep and grow their business.
Easier scalability: A repeatable compliance process lets you onboard new partners without rebuilding your workflow each time.
The opposite is just as important. Non-compliance costs add up in places that are easy to miss: staff time spent investigating rejections, delayed payment while invoices are corrected, expedited shipping to make up for late orders, and the harder-to-measure damage of being seen as a difficult supplier. Even when each incident is small, repeating them across many partners and documents makes compliance a clear business priority.
Industry-Specific EDI Compliance Requirements
EDI compliance requirements vary by industry because each sector exchanges different documents and answers to different rules.
Retail EDI Compliance
Retailers typically publish detailed supplier requirements, often called an EDI mandate. These cover purchase orders (850), advance ship notices (856), invoices (810), and tight timing and labeling rules. Suppliers are commonly scored on accuracy and on-time delivery, and missed requirements can lead to chargebacks.
Retail compliance also reaches beyond the EDI file. Many retailers require scannable shipping labels with serial shipping container codes (SSCC), and expect the data in the advance ship notice to match what is physically on the pallet. A correct 856 paired with a wrong label can still trigger a penalty, so align your warehouse and EDI teams.
Healthcare EDI Compliance
Healthcare EDI is shaped by HIPAA, which sets standards for electronic transactions and for protecting patient information. Common transactions include the EDI 837 claim and the EDI 835 payment advice. Compliance here covers both the transaction format and privacy and security safeguards.
Healthcare organizations also have to think about who may see the data. Access controls, audit logs and agreements with business partners all form part of staying compliant, and a document that is formatted correctly but handled insecurely is still a compliance failure.
Transportation and Logistics EDI Compliance
Carriers and shippers rely on documents such as the EDI 204 load tender, the EDI 210 freight invoice and the EDI 214 shipment status message. Compliance depends on timely, accurate status updates, because late or wrong messages disrupt tracking and billing.
Carriers are often measured on how quickly and accurately they report shipment events. Because status messages feed tracking portals and customer notifications, a delayed or inconsistent 214 creates problems well beyond the EDI team.
Manufacturing EDI Compliance
Manufacturers exchange forecasts and release schedules with suppliers and customers, using documents like the EDI 830 planning schedule and the EDI 862 shipping schedule. Compliance protects production plans and just-in-time delivery commitments, and the EDI 824 application advice reports errors back to the sender.
Manufacturers also work with long planning horizons. Forecast and release documents change frequently, so a compliant process needs to handle revisions cleanly and keep an accurate record of what was communicated and when.
EDI Security and Compliance
Compliance also includes how data is protected in transit and at rest. Common requirements include encrypted transmission (for example AS2 or SFTP), secure partner authentication, audit trails showing when each document was sent and acknowledged, and defined data-retention practices. In regulated industries such as healthcare, these controls are a legal obligation as well as a partner requirement.
A practical security baseline for EDI includes:
Encrypting data in transit with protocols such as AS2 or SFTP, and at rest where policy requires it
Authenticating partners with certificates or keys, and rotating them before they expire
Restricting who can view, edit or resend EDI documents
Keeping a searchable audit trail of every document, acknowledgement and error
Defining how long documents are retained and how they are securely deleted
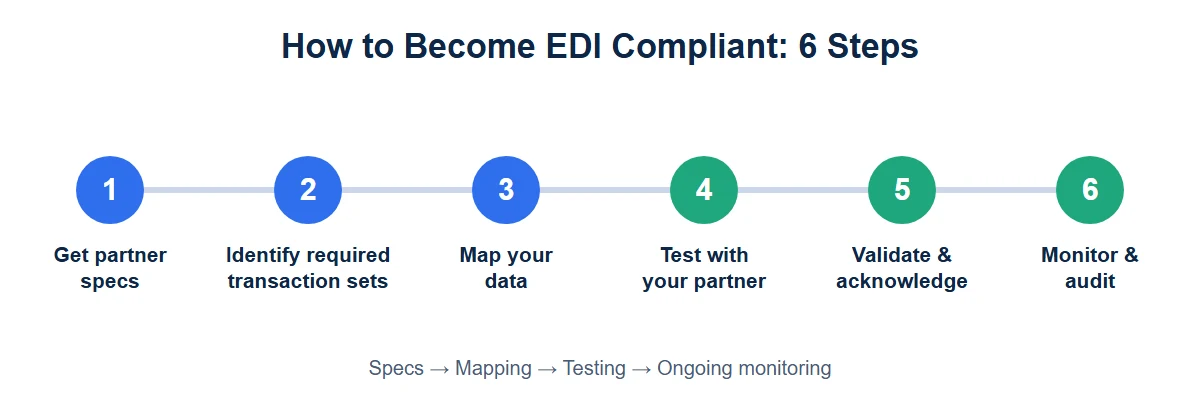
How to Become EDI Compliant: 6 Steps
If you are a supplier asked to become EDI compliant, or you are onboarding a new trading partner, follow this process:
Get the partner's EDI specifications. Request the implementation or mapping guide and any supplier compliance manual.
Identify the required transaction sets. Confirm which documents you must send and receive (850, 856, 810 and so on), and in which standard and version.
Map your data to the partner's format. Match fields from your ERP, WMS or accounting system to the required segments, qualifiers and code values.
Test with your partner. Exchange test documents and resolve differences before going live. Many partners require formal certification.
Validate and acknowledge. Add automated validation before sending, and send and process acknowledgements such as the 997 and 824 so errors surface immediately.
Monitor and audit. Track rejections, late documents and scorecard results, keep audit logs, and update mappings when a partner changes its specification.
Doing this by hand for every partner is slow and error-prone. An EDI solution like Astera EDIConnect lets you build partner-specific mappings visually, validate documents automatically, and monitor transactions in one place, so staying EDI compliant takes less effort as you add partners.
EDI Compliance Checklist
Use this checklist when you onboard a partner or review an existing connection:
I have the partner's latest specification and know which version it is
I know every transaction set I must send and receive
Required fields, qualifiers and code values are documented for this partner
My mapping handles optional and conditional segments the way the partner expects
Documents are validated automatically before they are sent
Control numbers are generated and tracked centrally
Acknowledgements are sent, received and reviewed, with alerts for errors
Deadlines are monitored and late documents trigger an alert
Testing or certification is complete and recorded
Security controls and audit logs are in place
Someone owns the process and is notified of specification changes
Challenges of Maintaining EDI Compliance
Reaching compliance once is manageable. Staying compliant is harder, for several reasons:
Many partners, many specifications: Each trading partner can differ on fields, codes and timing, so complexity grows with every connection.
Frequent changes: Partner updates and standard version changes can break a mapping that worked yesterday.
Manual processes: Re-keying data or fixing files by hand introduces errors and cannot keep up with volume.
Legacy systems: Older ERP and warehouse systems may not produce the data a partner now requires.
Limited visibility: Without monitoring, teams only find problems when a partner reports them.
Skills gaps: EDI knowledge is specialized, and it is easy to depend on one person who knows the mappings.
How Automation Simplifies EDI Compliance
Automation addresses these challenges directly. A modern EDI platform lets you:
Build and reuse partner-specific mappings visually instead of writing code
Validate every document against the standard and the partner's rules before it is sent
Handle acknowledgements automatically and route errors to the right person
Onboard new trading partners from templates instead of starting from scratch
Monitor all transactions in one dashboard and keep a complete audit trail
With Astera EDIConnect you can apply this approach to your own partner network, and reduce the manual effort that makes compliance expensive.
Book your personalized demo today and discover the transformative impact of EDIConnect
View Demo